HOW IT WORKS
The Strider approach
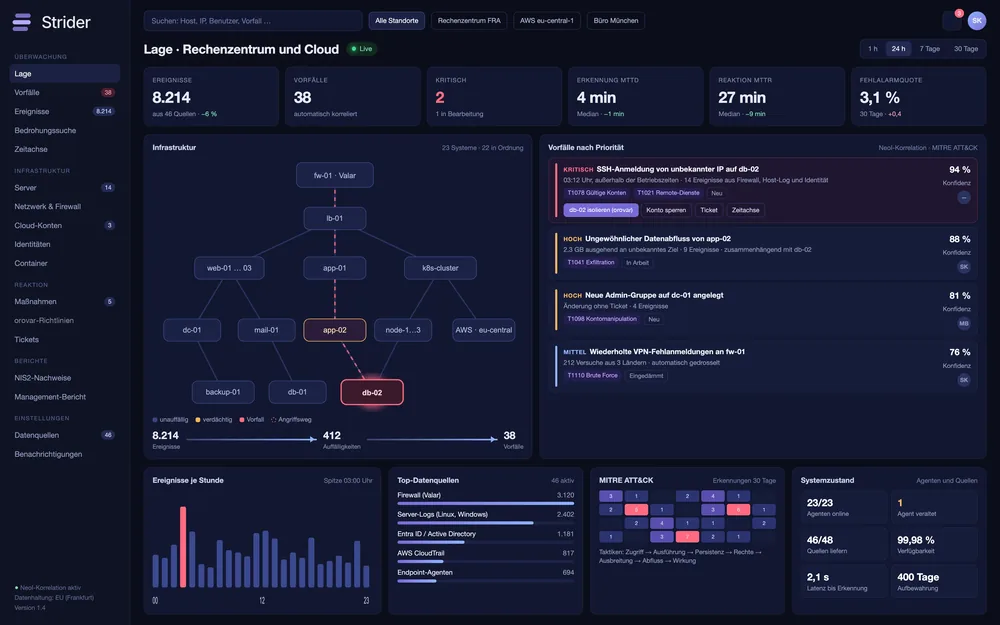
Strider consolidates signals from all relevant sources, automatically compresses them to incidents, and delivers the context required for fast decisions.
01
Signals from one place
Strider reads firewall logs (particularly from Valar), endpoint telemetry, identity provider events, cloud audit logs, and application telemetry. Data arrives in standardized formats and is normalized before correlation starts.
02
NeoI correlation instead of rule maintenance
Instead of a sprawling rule set that needs constant adjustment, Strider relies on trained correlation models. Related events are automatically grouped into one incident. An ongoing brute-force attempt across 200 endpoints appears as a single incident, not 200 separate alerts.
03
Prioritization with context
Every incident carries a severity, a confidence score, and a suggested next step. Analysts see why an incident was rated high priority and can review the reasoning in plain language.
04
Two views, one truth
Strider provides a technical SOC view for analysts and a consolidated situational view for leadership. Both work on the same data, so there is no discrepancy between technical reporting and management metrics.