EN

Cybersecurity Suite

Valar

Hardware firewall solution, Engineered in Europe.

The perimeter isn't dead. It has become European.

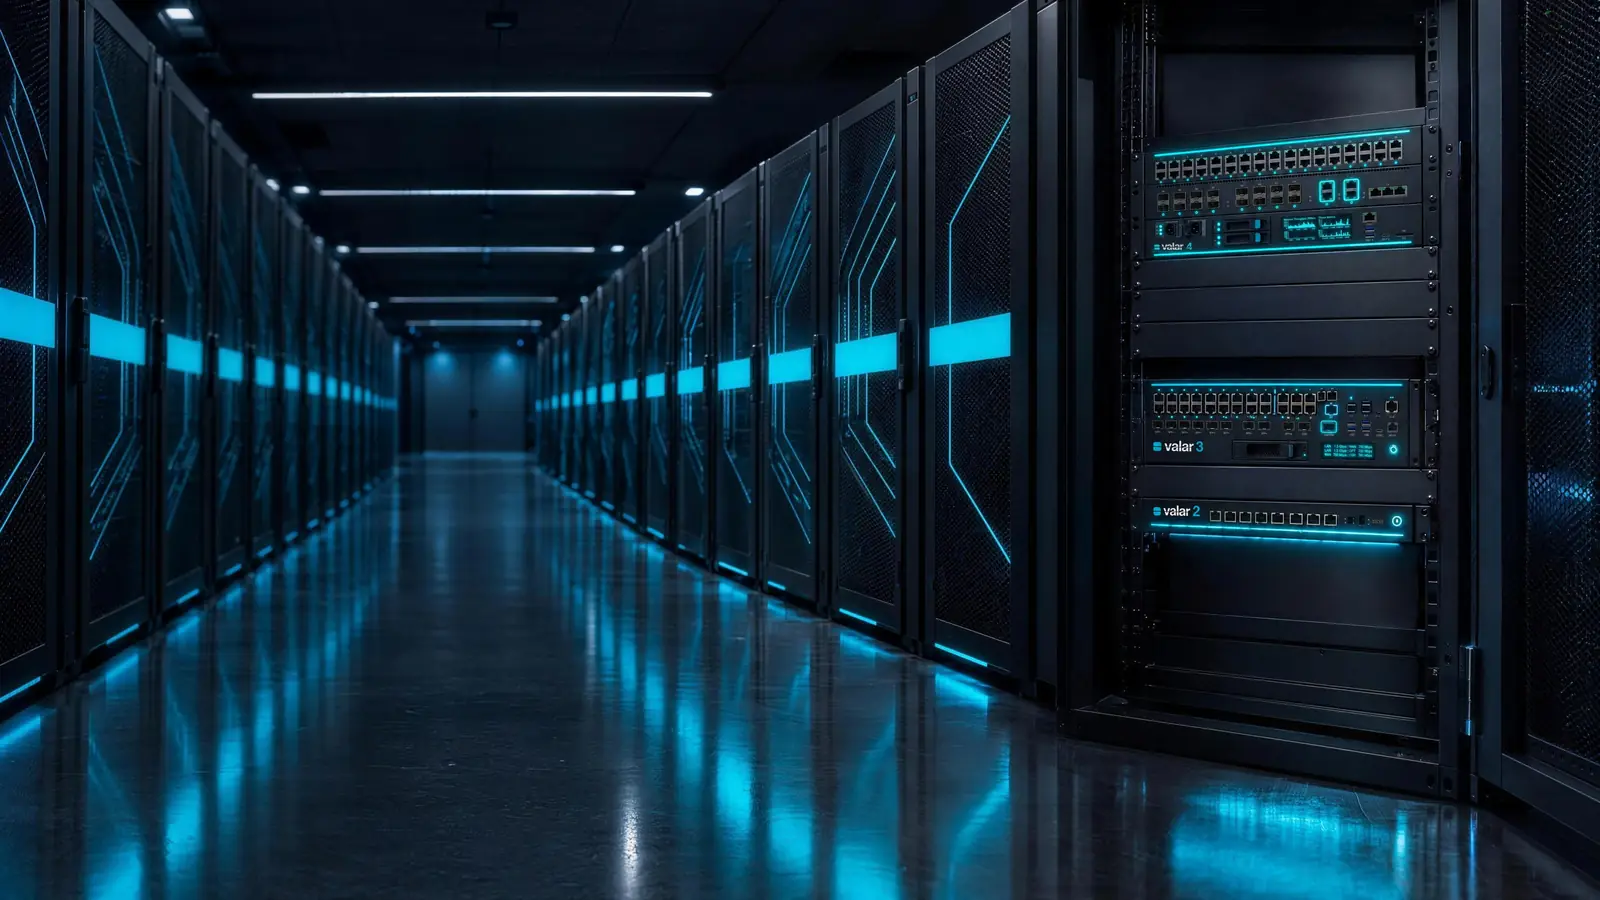
Data center with server rows, a Valar appliance in the rack on the right.

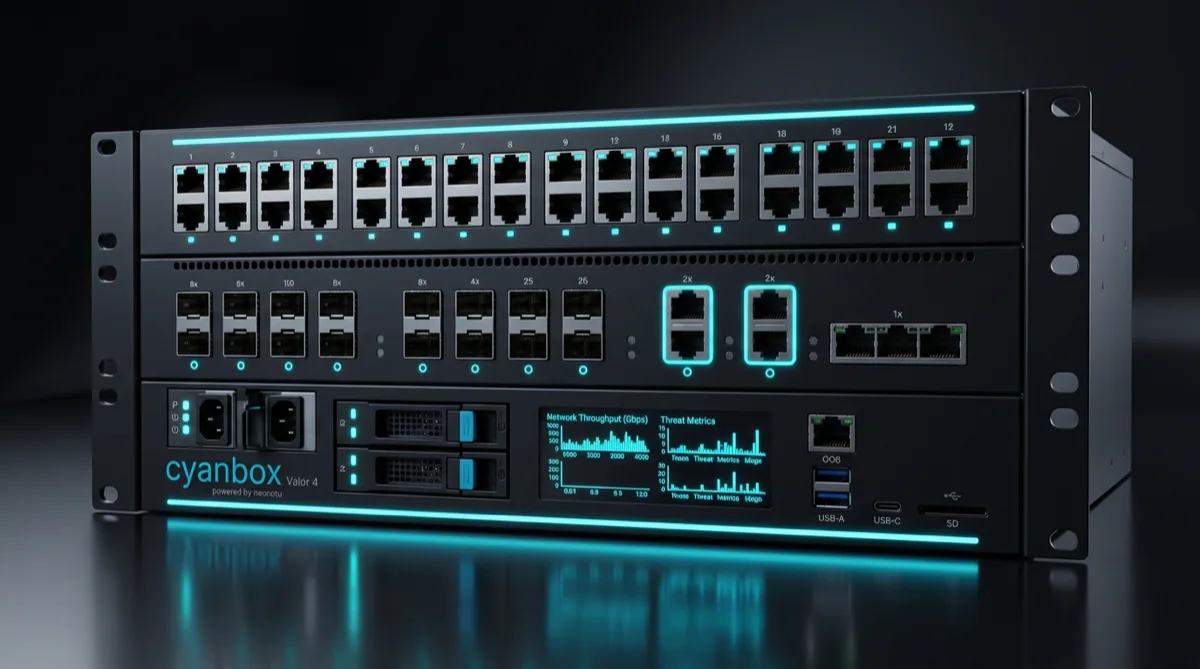
Valar is the hardware firewall line of the Cybersecurity Suite. The appliances secure the network perimeter and internal zones of an organization across four tiers — from a single medical practice to enterprises with several thousand seats.

What it changes

01

Clear sourcing

Hardware, software, and support from one source, with a traceable supply chain.

02

Scale without break

From the S model to an XL cluster, the management logic stays the same.

03

AI as default

NeoI (neonotu Intelligence) is part of every model. Detection quality improves with every update.

04

Sovereignty, documentable

Contractual and technical sovereignty can be evidenced in procurement files.

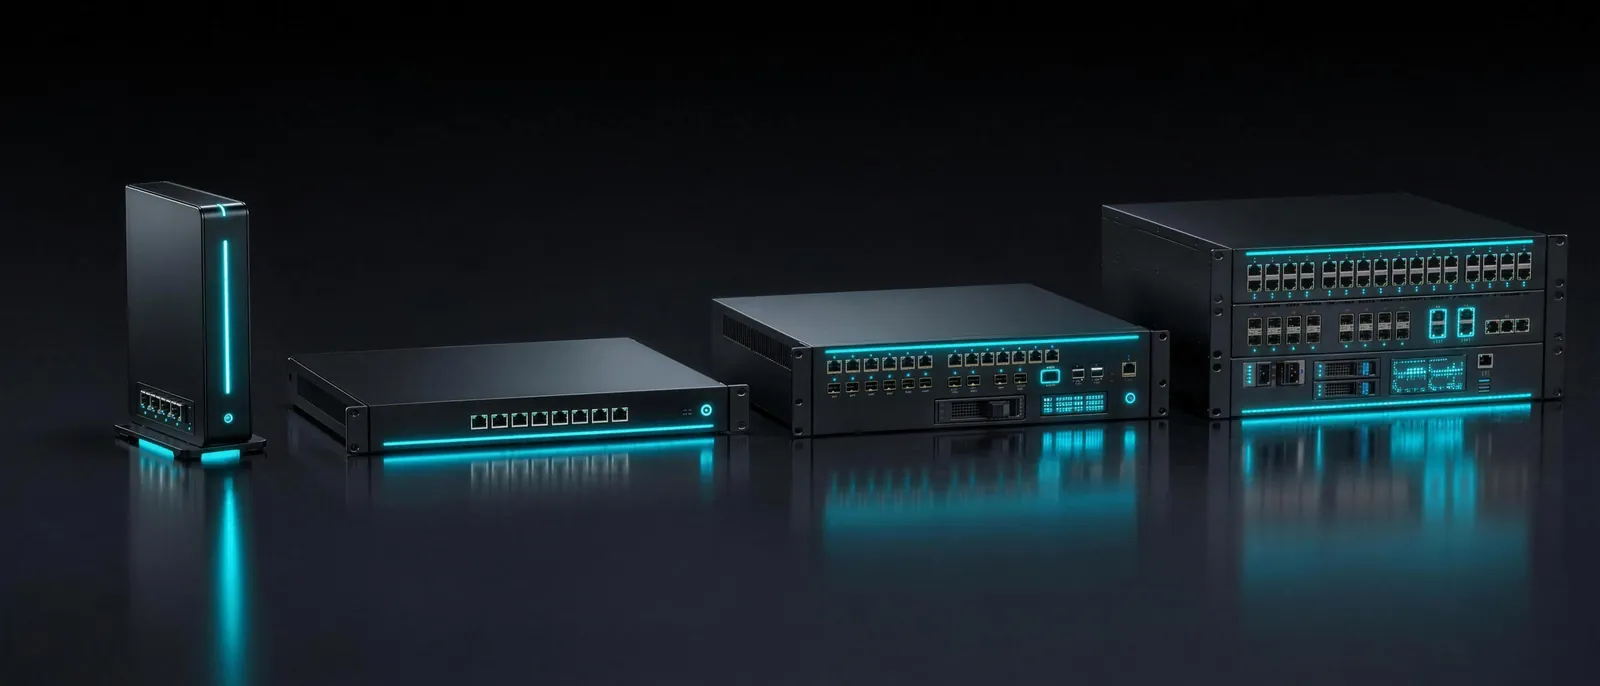
Cybersecurity, Engineered in Europe: four appliances, one platform, no US dependencies. The four models Valar 1 to Valar 4 side by side.
Four models, one platform.

HOW IT WORKS

The Valar approach

Valar rests on three principles: a clearly tiered hardware portfolio, a deeply integrated AI engine, and European sovereignty over engineering, software and data.

01

A model portfolio, not one-size-fits-all

Four hardware lines cover the range from a single site to a distributed enterprise network. Each model is tuned to the typical load profile of its target segment. No artificially crippled appliances, no overpriced entry tier.

02

NeoI as the core engine

Unlike purely signature-based approaches, Valar uses the NeoI engine to detect novel attack patterns. Behavioral analysis, anomaly detection, and threat intelligence from global telemetry feed into daily updates.

03

Developed in Europe

Engineering, software and data residency sit in Europe: operating system, ruleset, detection and management come from us, and the data stays in the EU. The appliances are manufactured to our specification, and the supply chain is documented and evidenced. That removes the risks from the U.S. CLOUD Act and opaque ODM arrangements where they count — in software, updates and data.

04

Licensing without module cascades

Functions such as IPS, SSL inspection, VPN, and web filtering are included in the base license. Licensing scales with model and term, not with a catalog of separately purchased function bundles.
MODELS

Four models for four scales

The tiering follows realistic usage patterns of European organizations. Cluster configurations enable high availability and effectively unlimited scaling beyond a single appliance.

Valar 1

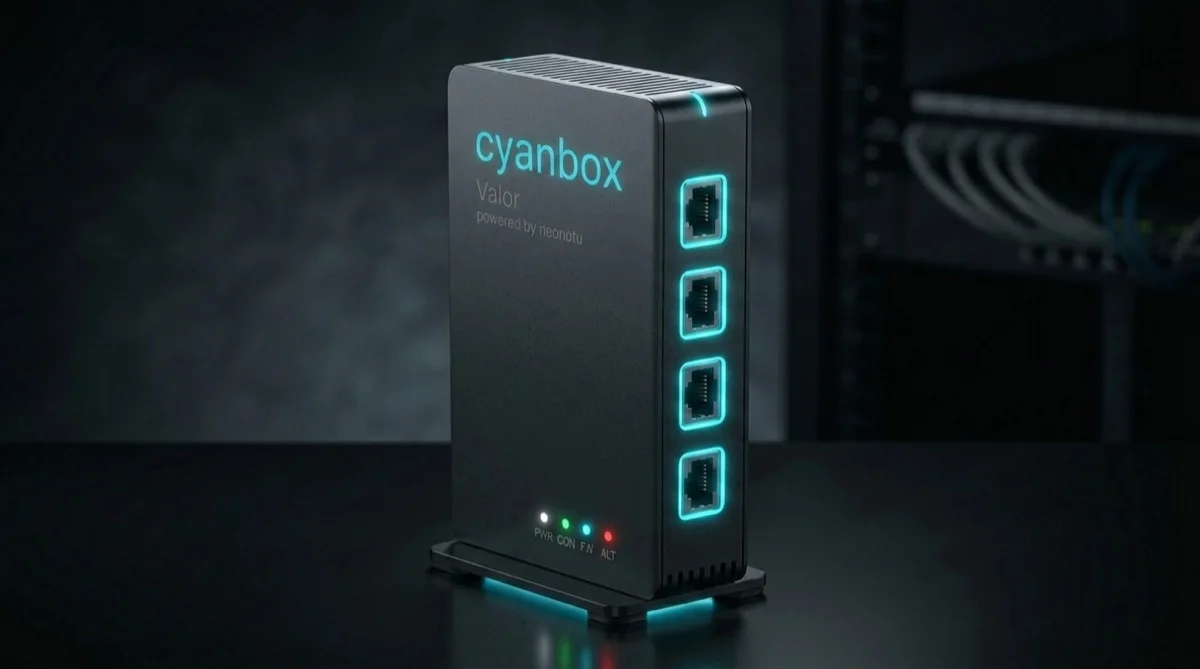
Valar 1 Compact

Target scale
Up to ~25 users
Throughput
Up to 1 Gbps inspection throughput
Valar 2

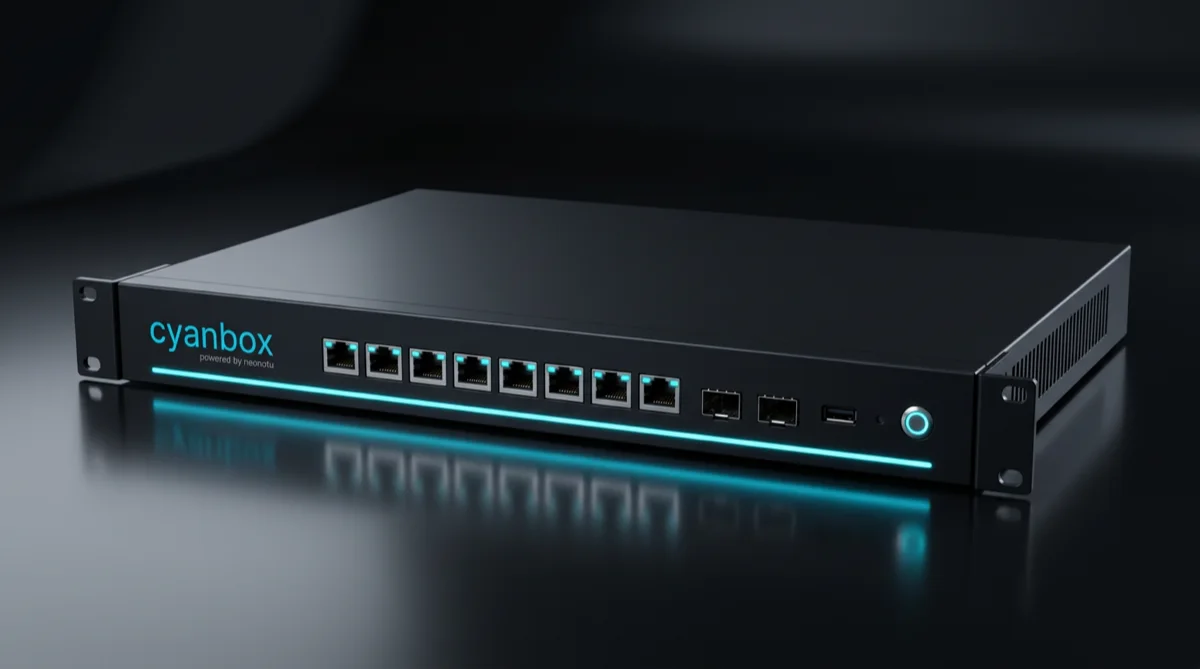
Valar 2 Business

Target scale
Up to 100 seats
Throughput
Up to 5 Gbps inspection throughput
Valar 3

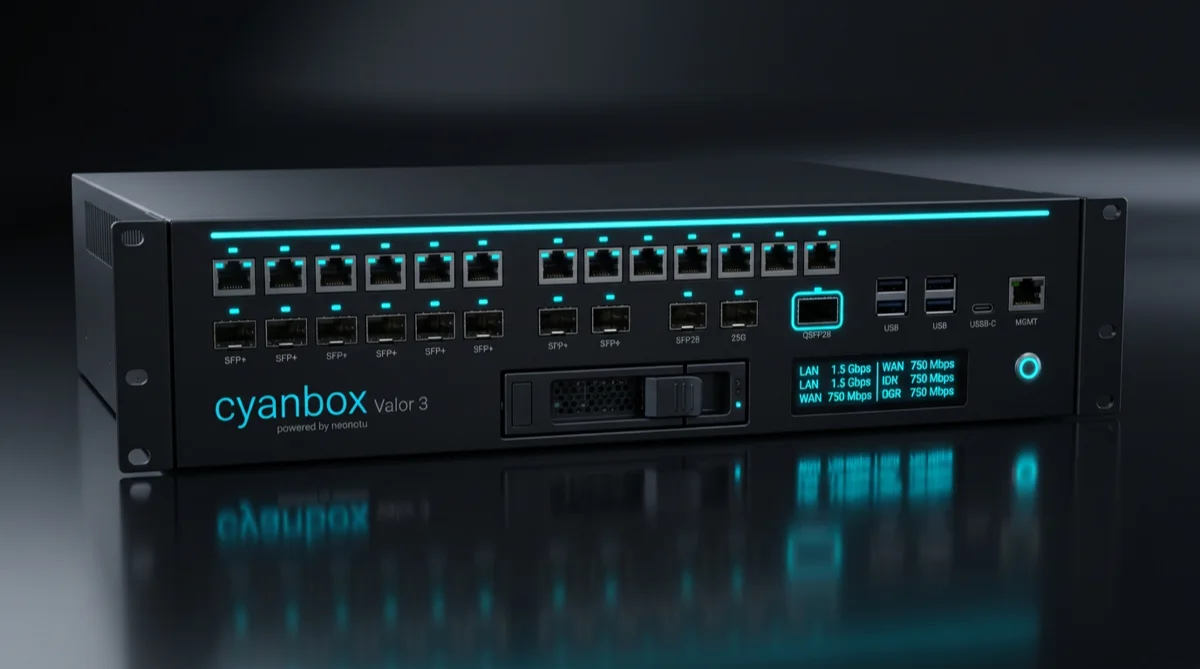
Valar 3 Enterprise

Target scale
Up to ~1,000 users
Throughput
Up to 20 Gbps, redundant PSUs
Valar 4

Valar 4 Critical

Target scale
5,000+, cluster-scaled
Throughput
Up to 80 Gbps, cluster-capable

In comparison

Market positioning

Valar competes with established vendors. The difference is not in individual feature checkboxes, but in architecture and sourcing.

Aspect U.S. standard vendors Valar
Feature scope Full Full
AI detection Variable, often cloud NeoI, on-device + cloud
Supply chain Opaque Documented and evidenced
Engineering Mostly U.S./Asia Europe
Data residency Often U.S. EU
Licensing model Module cascade Unified per model
KRITIS suitability Case by case Design principle

Typical deployments

Three example scenarios

Example scenarios of typical deployments in the European mid-market and the public sector.

01

Medical practice group

A practice group with 18 staff deploys Valar 1 at three sites. Central management enables uniform rule sets; access to medical specialist systems is secured via IPsec VPN. The NIS2 protection-need analysis is documented through the data already maintained in Sightadel.

02

Mid-sized mechanical engineering

A mechanical engineering firm with 240 employees replaces an aging firewall installation with two Valar 2 appliances in a high-availability cluster. The production zone is strictly separated from the office network; OT protocols are allowed selectively. SSL inspection is enabled for office traffic and deliberately disabled for production zones.

03

Regional KRITIS operator

A regional energy provider operates Valar 4 in a cluster across its two data center sites. European engineering and software, together with an evidenced supply chain, is what decides the internal KRITIS evaluation. Threat intelligence from NeoI feeds into the in-house SOC reporting.

NEXT STEP

Perimeter, reconsidered

Valar is the answer to a double requirement: technical parity with the established vendors, and a sourcing basis that fits European procurement, NIS2, and KRITIS.

For IT teams, this means a familiar product category with clear licensing logic and an AI engine that does not stop at the marketing label, but measurably contributes to detection quality. For leadership, it means a vendor that remains explainable in regulatory conversations.

Documents

Valar documents

Product information, white paper and data sheet as PDF. We will email you a personal link that stays valid for seven days.

Select documents

Get to know Valar

We will walk you through Valar in a personal conversation and answer your questions about deployment and next steps.

More products in the suite

Sightadel

NIS2, DORA, ISO 27001 and GDPR as preconfigured control catalogues, plus a security score from 0 to 100 across six domains. Dat…

View

Strider

Signals from firewall, endpoint, identity and cloud condensed into incidents instead of alert floods. NeoI correlation instead …

View

orovar

Detects, isolates and redirects to honeypots — in seconds, within a policy your organisation defines. Every action reversible a…

View

veyrisk

Vulnerabilities, attack surface, web applications, cloud and identities ranked by real risk. Active scans only with proof of ow…

View

Contact

Reputation takes years. Destruction takes seconds.

Talk to us before somebody else does. The first conversation is free and we reply the same business day.