HOW IT WORKS
The Sightadel approach
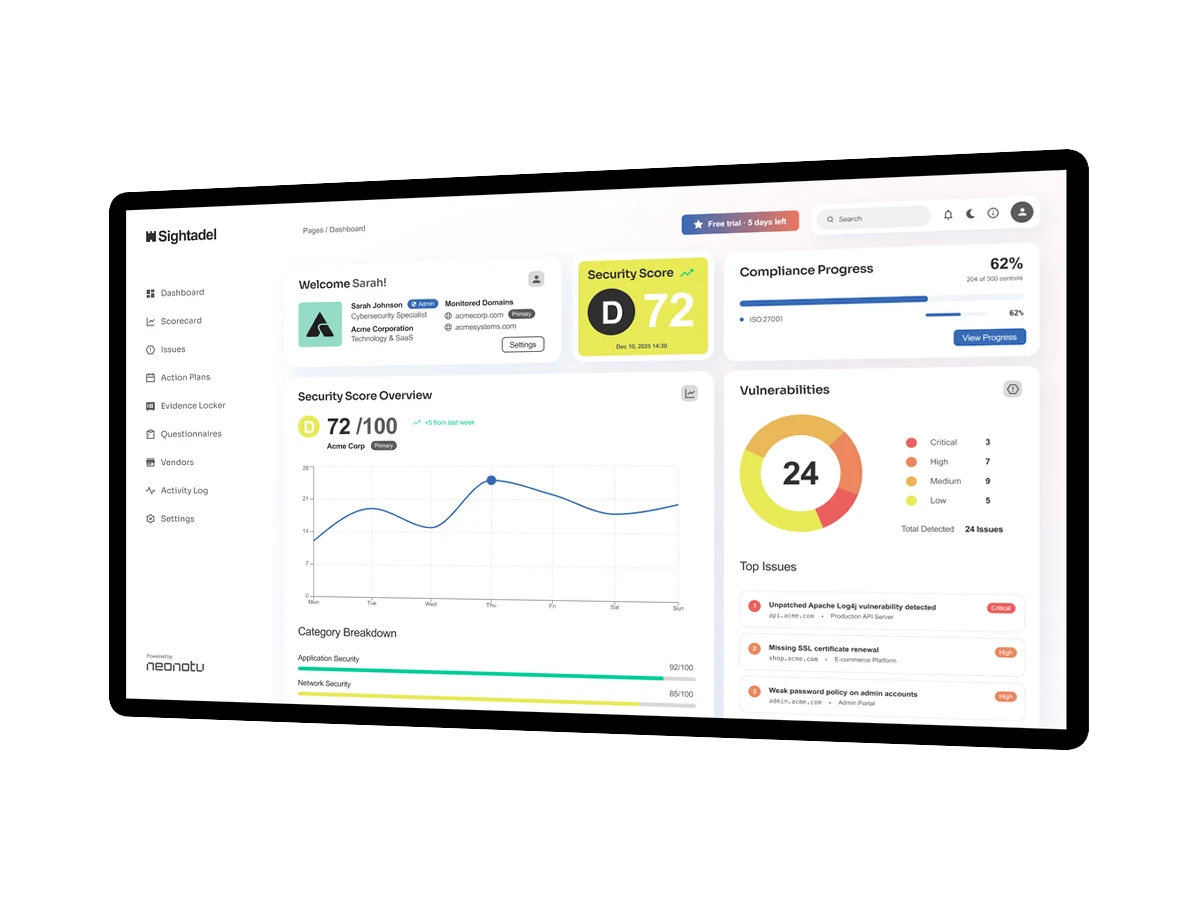
Sightadel combines three disciplines that have lived in separate tools until now: regulatory control catalogs, continuous technical evaluation, and shared scoring.
01
One platform for all relevant frameworks
NIS2, DORA, ISO 27001, and GDPR are integrated as pre-configured control catalogs. Controls are mapped across standards, so that a single measure (for example, maintaining an incident reporting process) satisfies multiple requirements simultaneously. Duplicate work disappears.
02
Continuous technical evaluation
Built-in scanners capture the external attack surface, check DNS and email configuration, identify exposed services, validate TLS certificates, and assess patch levels. The results feed into the security score and link automatically to the controls they affect.
03
A shared score from 0 to 100
The security score translates the combined picture of control coverage and technical reality into a single readable value. Leadership, IT, and external auditors recognize the posture and its trajectory at a glance.
04
Audit readiness as a by-product
Evidence is collected automatically and stored in audit-grade form. Reports for auditors, insurers, and leadership emerge at the push of a button, without dedicated audit-prep projects.