
External attack surface
Subdomains from certificate logs, DNS, TLS, admin interfaces, SPF and DMARC.
Exposure management
Servers, websites, cloud and identities. One list, ranked by real risk.
WHAT VEYRISK SEES
veyrisk starts with your domain and maps the rest on its own. Attackers don't ask for your asset list, they look at your company from the outside.
Subdomains from certificate logs, DNS, TLS, admin interfaces, SPF and DMARC.
Vulnerability management, continuous and agentless.
Your web applications tested for common weaknesses.
Configurations in AWS, Azure and Google Cloud.
Settings and risky accounts in Entra ID and Microsoft 365.
HOW IT WORKS
The passive scan starts right away. No contract, no agent.
From certificate logs, DNS, TLS and mail settings.
One DNS record. Only then do active scans run.
Only verified findings, ordered by real risk.
A follow-up scan proves each fix.
PRIORITISED
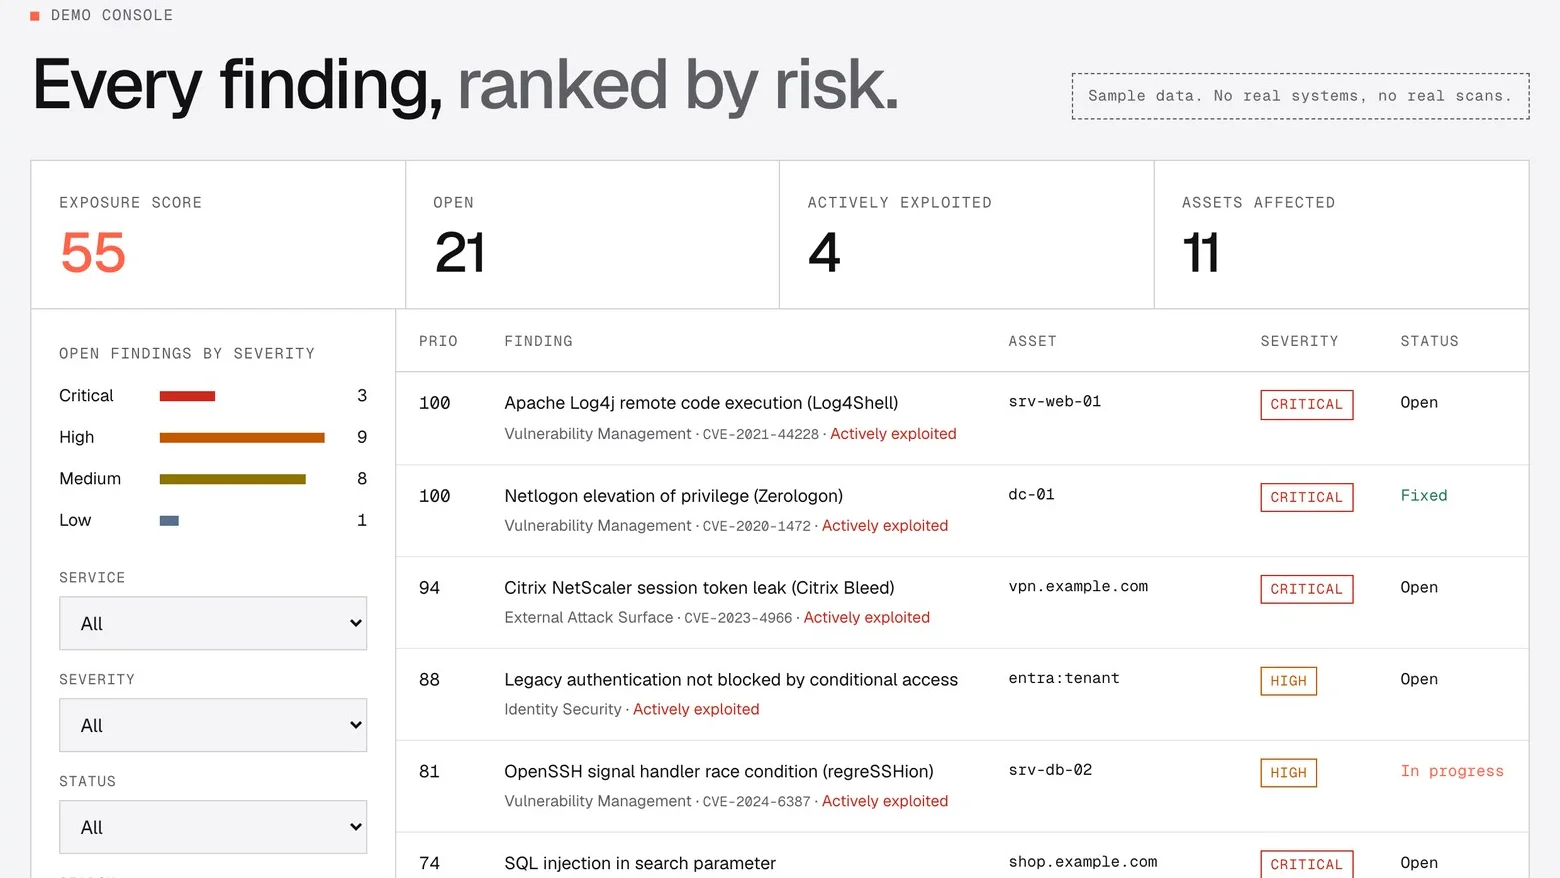
A classic scan report delivers thousands of findings, sorted by CVSS only, including test servers and retired systems. veyrisk ranks by severity, active exploitation and the weight of the affected asset. At the top is what an attacker would try first. If a check fails, veyrisk creates no finding.
START WITHOUT A CONTRACT
We show you the console with your own results. Operated in Germany, on our own servers.
Contact
Talk to us before somebody else does. The first conversation is free and we reply the same business day.