
A gift builds trust
Nobody suspects a rubber duck. Attackers count on that: curiosity and politeness move faster than any security policy.

A duck rarely comes alone
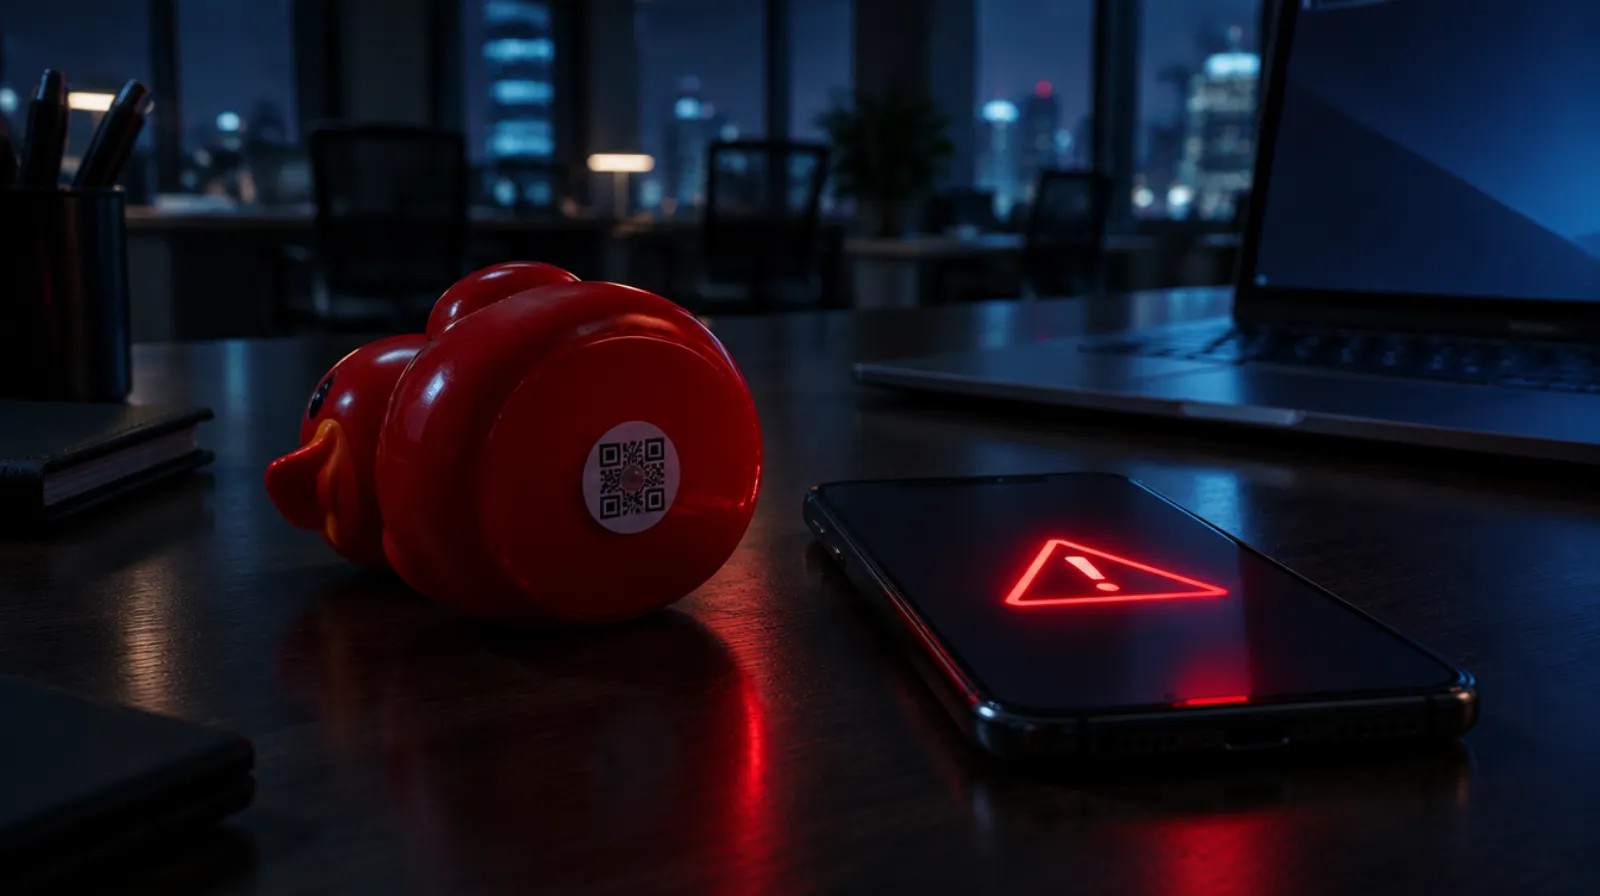
The duck arrived in the post, you scanned the code, and now you are here. An attacker would already have won at this point. Don't worry, this is not a real attack and nothing has happened to your device. But that is how easy it is.
WE HAVE ALREADY LOOKED AROUND
We had these details the moment this page opened, without asking a single question. Every website gets them. For an attacker this is step one: they now know which network you come from and which device you use. Next to it is the latest warning from our alert channel that matches it. They cannot tell whether your device is already updated. They can try, though.
Want to know what else an attacker can find out about your company?
THAT EASY
Bait that arrives by post or is left in the car park is an old trick, and it still works. Instead of a duck it is a USB stick, a promotional gift or a parcel with a QR code.
Nobody suspects a rubber duck. Attackers count on that: curiosity and politeness move faster than any security policy.
With a link in an email you can check the address first. With a QR code you only see it once the page is already open. Security people call this quishing.
The code is scanned with a phone, often over the mobile network. The filter in the company network never sees it. A real attack page would now have asked for your Microsoft 365 password.
WHEN IT GETS REAL
A real attack does not stop after the click. For every step, neonotu has a tool or a team that spots it or prevents it.
Before the attack, they look for open doors: forgotten subdomains, old login pages, an unpatched VPN gateway. veyrisk finds them first and tells you what to close first.
A fake login page captures the password. In our Security Awareness Training your team learns to recognise such pages, and quarterly phishing simulations show whether it has stuck.
With the stolen details they try to log in to the VPN or pull in malicious code. Valar blocks this at the edge. IPS, SSL inspection and web filtering are included in every licence.
If they do get in, they get noticed. Strider condenses thousands of events into a few incidents, and our SOC in Munich watches around the clock.
In an emergency our incident response team is available around the clock. In Sightadel you record training, tests and measures straight away as evidence for NIS2 and ISO 27001.
EXAMPLES FROM YOUR INDUSTRY
One click in the design office, and production stops the next morning. Valar separates the office and production networks, and Strider flags unusual access before machines stand still.
Patient data is especially valuable to extortionists. Valar 1 is built for small sites with up to about 25 users, and the short awareness modules fit into a busy practice.
Client data, remote access and service providers with broad rights. Our SOC notices when an account is suddenly used differently, and the leak check shows which passwords are already circulating.
DORA requires evidence of training, testing and incident reporting. Sightadel brings that evidence together, and penetration tests and red teaming provide the proof.
An attack pays off most when revenue is highest. veyrisk keeps an eye on shop subdomains, certificates and login pages, including the ones forgotten at the last relaunch.
NIS2 and critical infrastructure rules require documented security. Valar is engineered in Europe and not subject to the US CLOUD Act, and Sightadel and our NIS2 consulting guide you through the requirements.
THE NEXT DUCK
One mandatory session a year changes little. Our Security Awareness Training runs all year: short online modules every month, real phishing simulations every quarter and an on-site workshop twice a year. The evaluation shows where gaps remain. And if you want to know how your organisation reacts to a real duck, we test it with a social engineering assessment.
NO REAL DANGER. THIS TIME.
In a short call we show you where your company is vulnerable and what to tackle first. You can keep the duck.
Contact
Talk to us before somebody else does. The first conversation is free and we reply the same business day.