Cybersecurity solutions from Europe
Daten dahoam.
„Dahoam“ is Bavarian for „at home“: our home is Munich, our hosting is in Germany, our development is in Europe.
neonotu . we never sleep
THE SITUATION
Not too few tools. Too many side by side.
A typical morning in a mid-sized company: the auditor asks about the state of ISO 27001, a customer wants to see NIS2 evidence, the vulnerability scanner reports 3,000 findings. And nobody knows exactly which servers, subdomains and cloud accounts are actually reachable from outside.
Cybersecurity rarely fails for lack of a tool. It fails because too many tools run side by side and none of them shows the whole picture. Meanwhile NIS2, DORA and the GDPR set tasks for which there is usually neither the staff nor the time.
THREE BUILDING BLOCKS
Compliance, attack surface and perimeter from one source
Three products that fit together because they grew together, out of the daily work of a team that tests infrastructures, defends them and investigates incidents forensically.
The attack surface in view
Continuously checks servers, the web presence, web applications, cloud environments and identities such as Entra ID and Microsoft 365. Findings are weighted by severity, active exploitation and the importance of the asset rather than by a CVSS number that makes everything look equally urgent.
The perimeter, thought through in Europe
A hardware firewall in four models, from an office of around 25 users to critical infrastructure with more than 5,000. Development, software and data storage are in Europe. IPS, SSL inspection, VPN and web filtering are included in the base licence, with no add-on modules.
The suite also includes Strider for real-time security monitoring and orovar, an autonomous security agent.
NEXT STEP
Where does your company stand right now?
A conversation in which we go through your position: evidence, attack surface, perimeter. Afterwards you know what needs doing. With us or without us.
First conversation free, reply the same working day.
WHY LOCATION MATTERS
Security data is the most sensitive material a company holds
Open vulnerabilities, network diagrams, access credentials. At neonotu this data sits in Germany: Sightadel and veyrisk run at German hosting providers, not at a US hyperscaler.
The contracting party is neonotu GmbH, based in Munich. It is itself the parent company and not a subsidiary of a group outside Europe. European law therefore applies, including the GDPR and processing under Art. 28. There is no third-country dependency.
For companies that must guarantee data sovereignty to their own customers, that is not a marketing line but a clause in the contract.
- MunichRegistered office of neonotu GmbH
- GermanyHosting for Sightadel and veyrisk
- ISO 27001 + 9001neonotu is certified
- Art. 28 GDPRProcessing under EU law
THE WHOLE, NOT THE PARTS
Security a mid-sized company can actually steer
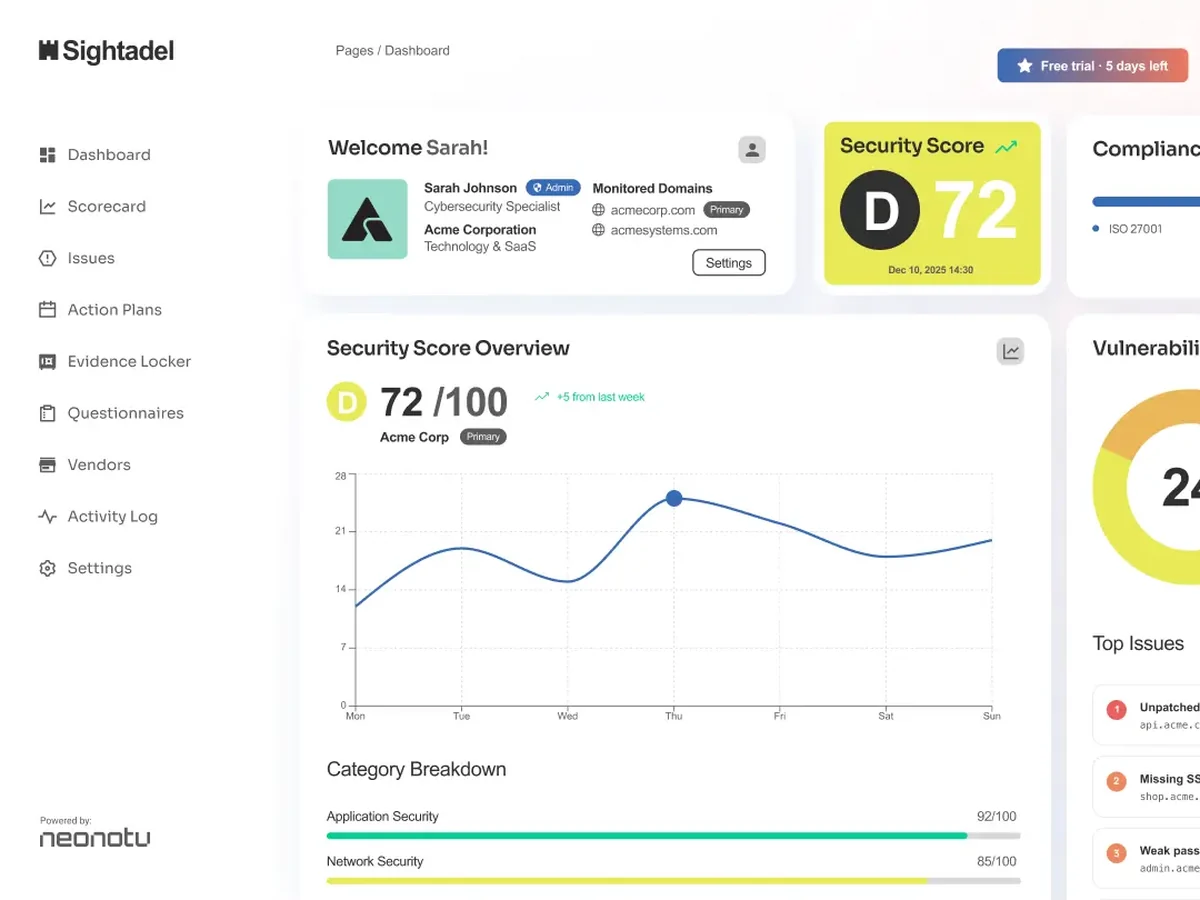
Sightadel shows what has to be evidenced. veyrisk shows where the company may actually be vulnerable. Valar protects the edges of the network.
Where tools alone are not enough, the neonotu team steps in with penetration testing, a virtual CISO or building an ISMS. Without the company having to stand up a security department of its own.
„We only claim what we can prove.“
Contact
Reputation takes years. Destruction takes seconds.
Talk to us before somebody else does. The first conversation is free and we reply the same business day.