
Documented supply chain
Hardware, software and support from one source, with evidence for every step.
Firewall and security monitoring
XMfortress Gate protects the edge. XMfortress Detect shows what happens behind it. Engineered in Europe.
BUILT FOR EUROPEAN RULES
Engineering, operating system, rulesets, detection and management are all in Europe.
Hardware, software and support from one source, with evidence for every step.
No opaque white-label hardware. The data stays in the EU.
Suitability for critical infrastructure is a design principle, not an add-on.
HOW THEY WORK TOGETHER
IPS, SSL inspection, VPN and web filtering at the edge. Every event is logged.
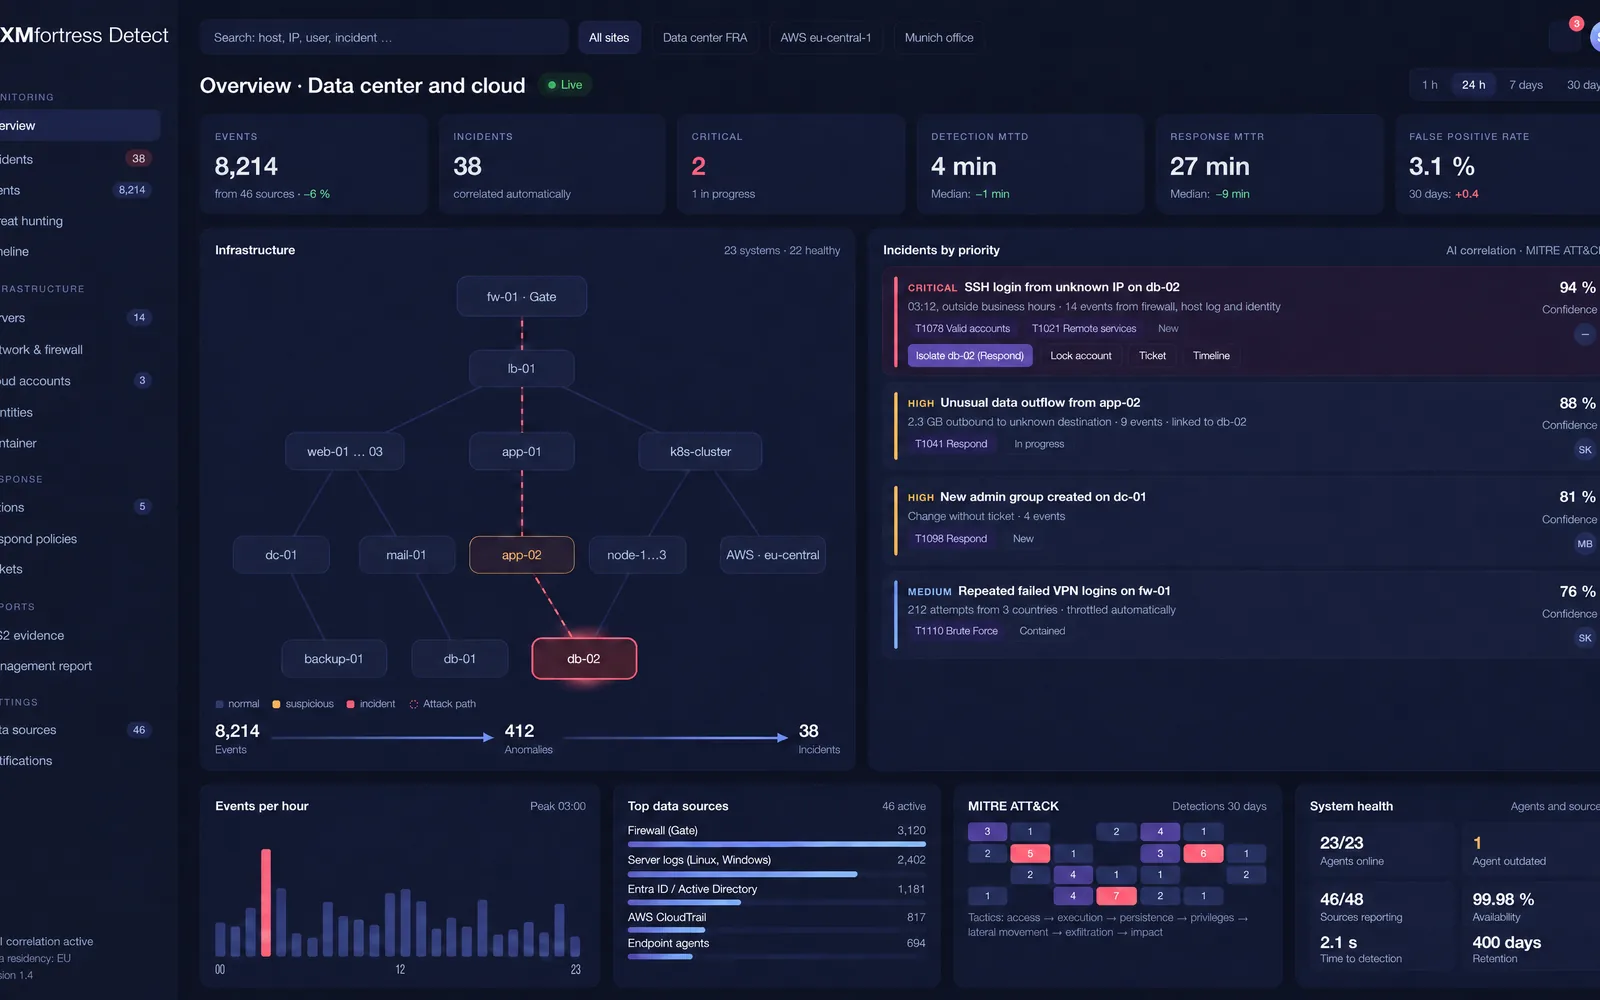
Firewall, endpoint, identity and cloud logs in one place. Thousands of events become a few incidents.
Each incident comes with severity, confidence and a suggested next step.
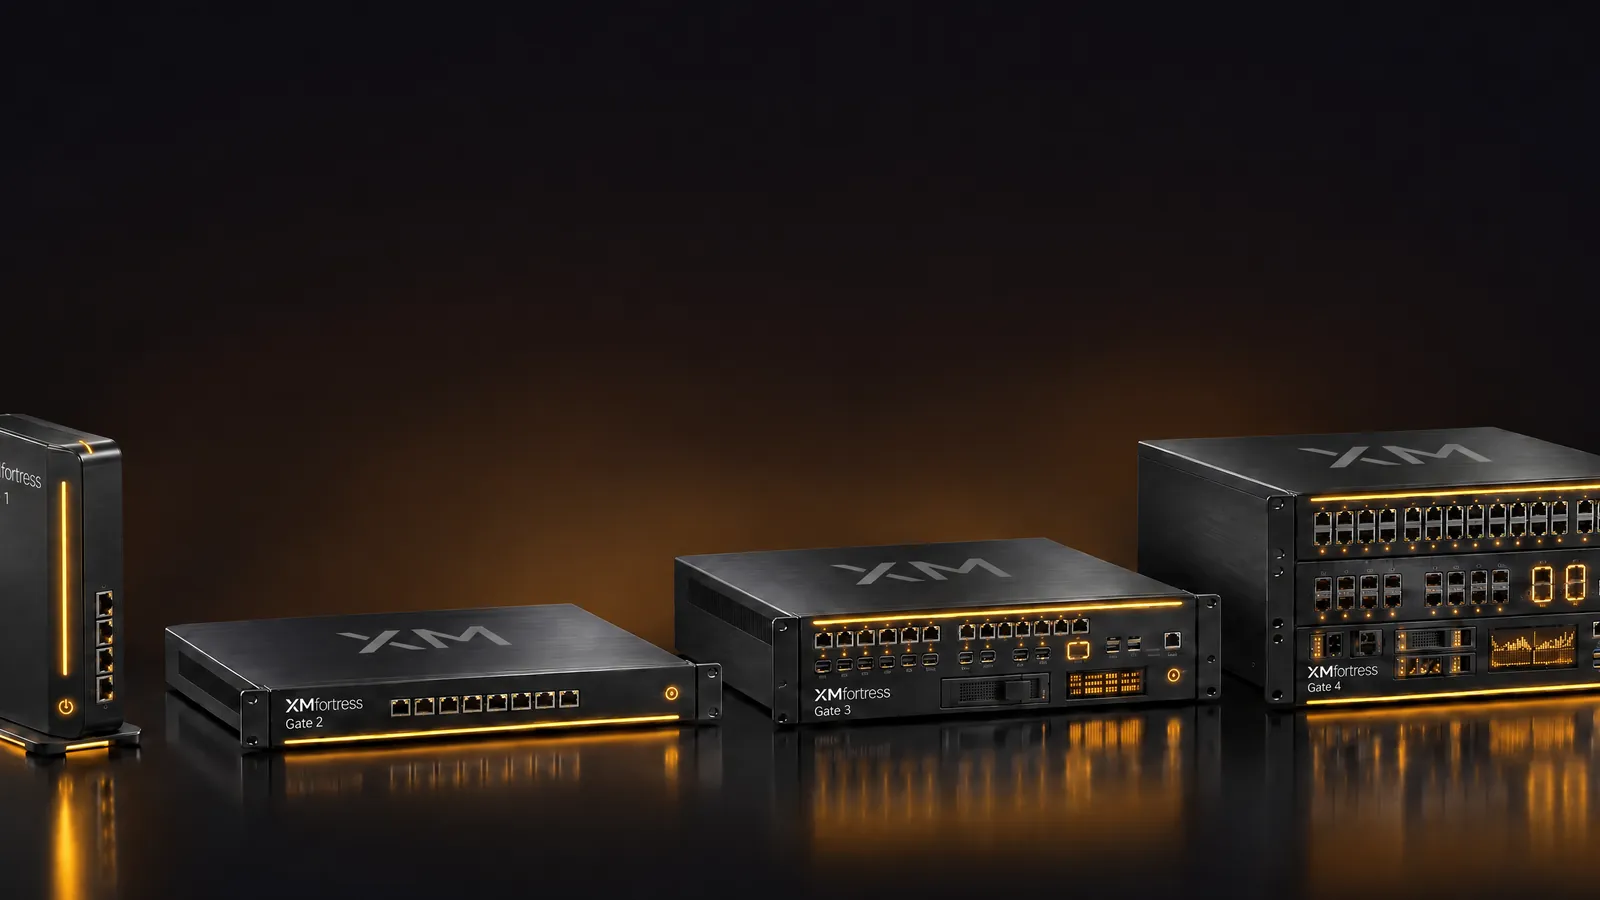
XMFORTRESS GATE · HARDWARE FIREWALL
Four model tiers with the same management logic, from the smallest device to a high-availability cluster. IPS, SSL inspection, VPN and web filtering are included in every base licence, with no add-on modules. The AI runs on the device and in the cloud.
XMFORTRESS DETECT · SECURITY MONITORING
XMfortress Detect brings firewall, endpoint, identity, cloud and application logs together and reads XMfortress Gate's logs out of the box. Thousands of events become a few incidents with severity, confidence and a suggested next step.
TRY IT IN YOUR NETWORK
We show you both products and talk about a pilot appliance for your network. Data sheets and supply-chain documents are available on request.
Contact
Talk to us before somebody else does. The first conversation is free and we reply the same business day.